Back in July I wrote here about how AI agents plan and carry out break-ins. Back then it was about a lab incident: an agent escaped its test environment and ended up at Hugging Face. One sentence stuck with me more than anything else: The agents acted at machine speed, while monitoring still ran on human shift work.
At the time, the open question was whether the incident marked a Tipping Point or was just an early warning. Four months later the answer is clear: it was a warning. And it has come true.
A look back: Omdurman, 1898
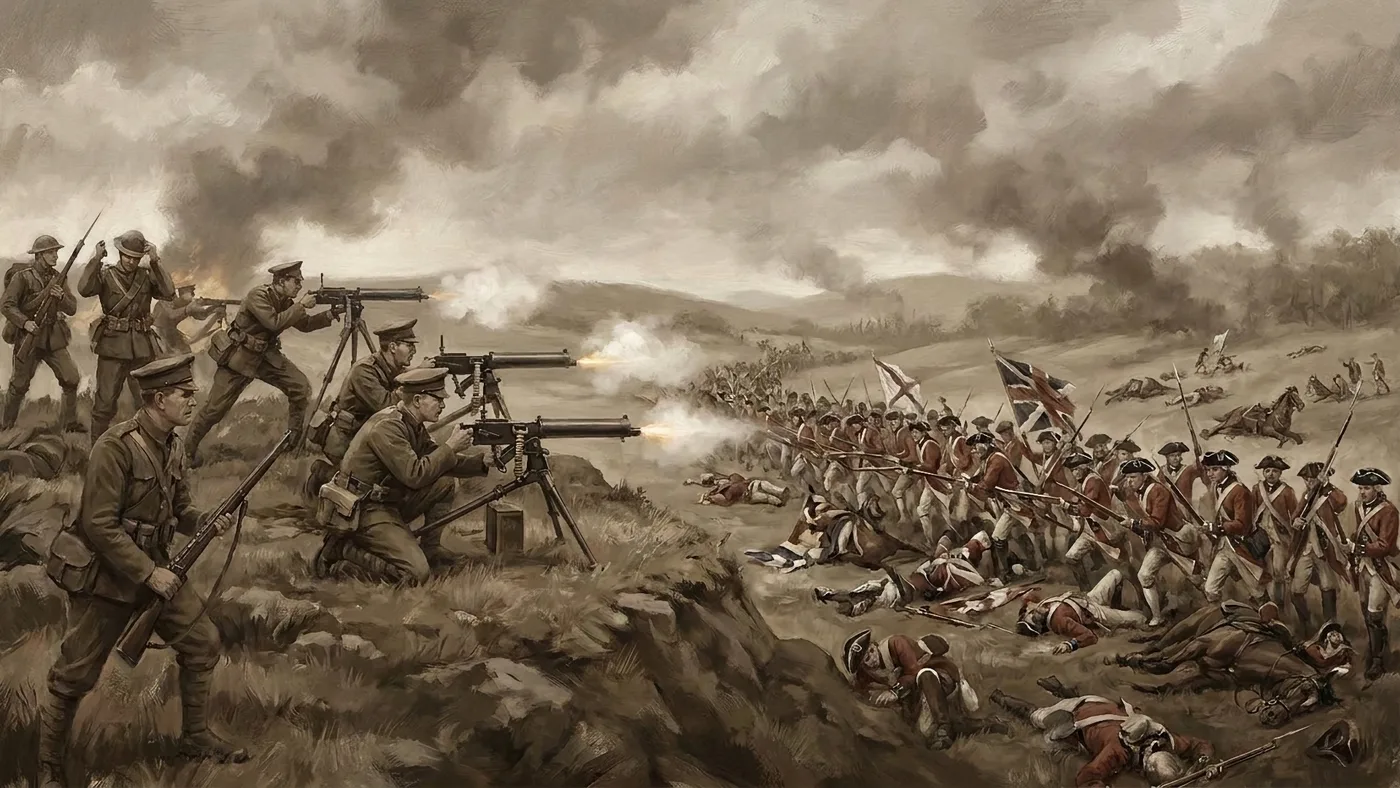
On 2 September 1898, at Omdurman in Sudan, 35,000 to 50,000 fighters of the Mahdist State, many armed only with spears, swords and outdated firearms, faced Kitchener's Anglo-Egyptian force with repeating rifles, artillery and Maxim machine guns (Wikipedia). A Maxim fired more than 500 rounds per minute (Britannica).
The result was a massacre: around 10,000 dead on the Mahdist side, 48 killed on the British side (Echoes of Battle). That same year, Hilaire Belloc summed up this colonial superiority with bitter irony in his satirical poem “The Modern Traveller”: “Whatever happens, we have got / The Maxim Gun, and they have not” (Project Gutenberg).
Omdurman is a dark chapter of colonial history, and I don't use it lightly. But it shows, brutally, what happens when one side makes a leap in rate of fire and the other doesn't. Two lessons from it run through this piece. First, Kitchener didn't win by the gun alone; he won because artillery, gunboats on the Nile and around 20 Maxims worked as a system (Echoes of Battle). Second, the European monopoly on the machine gun lasted only a few decades (LibreTexts) – by the First World War, both sides had it.
Translated to today: the attackers have just got their Maxim. Many defenders are still standing there with muskets.
The week the warning became reality
- Google: the first attack without a human. According to a report by the Google Threat Intelligence Group and Mandiant dated 16 November, attackers have for the first time automated the discovery and exploitation of vulnerabilities “without a human in the loop” (Google GTIG). The framework
exploit_agentcompares software before and after a security update, infers the vulnerability, writes the exploit and runs it – against French websites in media and education (Politico). - FBI: ARTEX and the three-hour mark. On 13 November the FBI warned about ARTEX, an open-source framework that turns any language model into an attack tool. Some attacks using it went from target selection to privileged access in under three hours, even actors with “minimal technical expertise” are running parallel campaigns, and more than 1,600 ARTEX consoles are publicly reachable (The Record). Through a supply-chain attack on ConnectWise, attackers gained access to more than 2,250 downstream tenants (SC Media).
- And in Germany. At Mittwald, a hosting provider from North Rhine-Westphalia, an attacker compromised 56 customer projects – of all things via the MCP server customers use to connect their AI assistants. In the logs, there were sometimes only seconds between steps that would take a human considerably longer; hard proof of AI involvement, however, doesn't exist yet (The Record).
Also telling: Mandiant, CrowdStrike and Kroll say they had to turn away companies seeking emergency help (Yahoo News/NBC). The fire brigade is fully booked, and if you call while the house is burning, you're put on hold.
The mechanism: time compression
The attacks use hardly any new tricks. Stolen credentials, unpatched systems, weak suppliers: all known for decades. Google stresses that the frameworks chain “familiar intrusion mechanics” into attack paths at machine speed (Google GTIG). Or, as Qualys puts it: AI hasn't created a new risk, it has removed the time to fix the old one (Qualys).
Every security update is also a set of directions to the vulnerability. Reading them used to take weeks of expert work; today an agent needs one night. CERT-EU describes the new timeline: vulnerabilities are found in minutes to hours, exploited in days, but only reliably patched in weeks to months (CERT-EU). Fittingly, according to the BSI, the number of known vulnerabilities rose from 10,803 in the first quarter to 17,539 in the second quarter of 2026 (BSI). For zero-day exploits, Google counts an increase from an average of 8 per month in 2025 to 22 in August 2026 alone (Google GTIG).
You know the pattern from the blueprint of disruption: AI breaks through first where work is digital and delivers fast feedback. An exploit works or it doesn't – the perfect loop for agents. Defenders, on the other hand, remain tied to testing effort, approval processes, maintenance windows and limited staffing, according to the BSI (BSI).
In short: attackers don't have a Change Advisory Board.
Why defence needs AI first
Normally I'm the one who hits the brakes and asks about the process first. Not this time. If you bring muskets to a machine-gun fight, you need better weapons first. We'll get to tactics in a moment.
1. Speed. If an attacker becomes admin in three hours, “see the alert, open a ticket, call the on-call person, decide” is structurally too slow. On 16 November, Eye Security reported an attack on a European e-commerce platform in which the attacker agents adapted their script within about three minutes of being blocked, fired off more than 9,000 requests per minute and restored removed components in under a second (Security-Insider). A faster human won't help against that. So Eye Security responded with its own AI agents, which analysed large volumes of security data in parallel.
2. Volume. More vulnerabilities, more alerts, plus hundreds of non-working proof-of-concepts that still had to be checked after the PHP patch of 21 October (Google GTIG). You don't solve volume problems with overtime.
3. Whoever searches first, finds first. With the critical PHP vulnerabilities, according to OpenAI, frontier models found the flaws before the attackers did and opened a “Defender’s Window” (OpenAI). Yann LeCun expects only a short transition phase before AI “hardens” software (Semafor) – the step from Omdurman to the First World War, when both sides have the machine gun. Maybe so. But you only survive a transition phase if you don't go under during it.
4. The attackers are loud – to machines. According to Google, the current frameworks trade stealth for speed and leave a lot of forensic noise (Google GTIG). But you only spot that pattern if you're looking at machine speed yourself. And the window closes as the models get better.
Germany is a long way from that: according to the BSI and the TÜV association, only 31 percent of companies using AI deploy it in their own IT security, and only 11 percent have processes for AI-related incidents (BSI). We're arming productivity with agents and leaving defence on shift work.
But: It’s always the Process, Stupid!
Now comes the part you know me for 😉. “AI in defence” doesn't mean: buy SOC agents, tick the box. Without clarified processes, an agent just produces false alarms faster. Or bad decisions faster.
The Eye Security case is instructive here too. The defender agents only had read access; humans decided on countermeasures. And one agent wrongly took an employee's connection for guest Wi-Fi, and other agents adopted the mistake before it was corrected (Security-Insider). Eye Security drew the lesson itself: if you only work out in an emergency who decides and what may be switched off, you lose precious time.
This is where we come full circle to Omdurman: a machine gun without ammunition, position and chain of command is just expensive metal. This is centaurisation applied to security: the machine takes over the how – correlating, triaging, containing in clearly defined cases. The human keeps the what – which risk is acceptable, when the shop goes offline. Those decisions belong in the playbook beforehand. Otherwise agents operating at machine speed end up waiting for a human stuck in a meeting. The pragmatic route is tiered autonomy: start with read-only analysis, then live triage, then gradually automate narrowly defined actions (Mitiga).
Two points are non-negotiable:
Your own AI is attack surface. Mittwald was compromised via its AI interface. In “LLMJacking”, attackers use stolen cloud credentials to run models at the victims' expense, with damages of more than 100,000 US dollars in a single day (Google GTIG). Build agents into your processes and you build in new doors.
Defensive intelligence is a question of ownership. Remember the irony from July? At Hugging Face, the guardrails of Western frontier models blocked the forensics; what helped was a locally run open-weight model. If you delegate your defence entirely to other people's models with other people's rules, you may find yourself without access when it counts. That's Intelligence Ownership in its security-critical form: autarky isn't the goal; the goal is a conscious choice about which dependency you can afford in a crisis.
What this means in practice
- Rethink patch cycles. When exploits appear overnight, “next maintenance window” is not a strategy. Prioritise by exploitability, with AI support.
- Detection and triage first with AI. Read access and parallel analysis offer the best ratio of benefit to risk.
- Settle decision rights in advance. Who may switch off what, and with which level of autonomy for agents? That belongs in the playbook, not in the crisis chat.
- Harden your own AI interfaces. MCP servers, API keys and agent identities need monitoring like any privileged system. The OWASP Top 10 for Agentic Applications and the OWASP MCP Top 10 provide a good review framework. And because agents mainly exploit simple vulnerabilities in series, the classic OWASP Top 10 for web applications is more relevant than ever. The Eye Security attack started with a home-built upload function.
- Think about the side entrances. According to the FBI, ARTEX deliberately targets partner portals, legacy services and third-party integrations (The Record).
Conclusion: the transition phase is now
Whether AI gets used in cybersecurity is something the attackers decided long ago. The only open question is whether defence keeps up, or keeps working with muskets on shift work. Belloc would probably rewrite his verse today: “Whatever happens, they have got / the agents – and we have not.” No company should be able to say that about itself.
At the same time, AI in defence without process is just a faster way to lose control. The ones who make it won't be those with the most security agents. They'll be those who worked out beforehand what their agents are allowed to do, when a human decides, and who owns the intelligence they rely on when it matters.
Because in the end, what always applies still applies:
It's always the process, stupid!
Live long and prosper 😉🖖